Cisco Secure Email Gateway Zero-Day CVE-2026-76519 Under Active Exploitation; Allows Root-Level Command Execution
Cisco said attackers are actively exploiting a zero-day vulnerability in Cisco Secure Email Gateway that can let unauthenticated remote attackers write arbitrary files and execute commands with root privileges. The vulnerability, tracked as CVE-2026-76519, affects appliances with specific Advanced Malware Protection and Content Scanner Tools configurations, and Cisco released its initial advisory on October 14, 2026. Key Points CVE-2026-76519 is…
Ledger Wallet Hack: Hardware Implant Linked to $86M in Crypto Losses
Ledger is investigating reported cryptocurrency losses in Southeast Asia after confirming that one device belonging to an affected user contained an unauthorized hardware implant. Pseudonymous blockchain investigator Specter estimated that losses exceeded $86 million across Bitcoin, Ethereum, and Tron, while Ledger described the confirmed cases as limited and said the incident appeared isolated to one reseller and its Southeast Asian…
Google Pays XBOW $250,000 for Chrome Exploit Using CVE-2026-85045 and CVE-2026-78952, Potentially Affecting 1B Windows Users
XBOW said on October 13, 2026, that Google paid it $250,000 for a Chrome full-chain exploit that combined three previously unknown chrome vulnerabilities. Loading a malicious web page could have given an attacker code execution outside Chrome’s security sandbox without requiring a click or download, although Google reproduced the chain, fixed the vulnerabilities and XBOW said it was never used…
Attackers Exploit Ivanti Connect Secure CVE-2026-104935 Zero-Day for Unauthenticated Remote Command Execution
Ivanti Connect Secure is affected by a high-severity zero-day vulnerability that attackers exploited before its October 13, 2026, disclosure, enabling remote unauthenticated command execution on vulnerable VPN appliances. Ivanti said exploitation affected a limited number of customers, while Volexity linked the activity to a previously unknown threat actor tracked as UTA0576 and found credential theft, Active Directory reconnaissance, and preparation…
GitLab Patches CVE-2026-97229 in CI/CD Regex Compiler, Enabling Unauthenticated RCE on Self-Managed CE/EE Servers
GitLab has patched CVE-2026-97229, a CVSS 10.0 integer-overflow vulnerability in the CI/CD regular-expression compiler that could allow an unauthenticated attacker to execute arbitrary code on a GitLab server through a specially crafted regular expression in a CI/CD configuration. GitLab released fixes for the vulnerability on October 12, 2026, and strongly urged operators of affected self-managed installations to upgrade immediately. Key…
Danfoss Remote Refrigeration Software Attack Spoils Food Across 400 French Stores
A cyberattack targeted remote refrigeration-control software used by French supermarket chains, allowing hackers to manipulate temperatures and defrosting functions in store cold units. More than 100 Coopérative U supermarkets and 180 stores operated by the Mousquetaires Group were affected, while figures supplied by individual retailers indicated that about 400 stores were hit across France. Key Points Hackers manipulated supermarket refrigeration…
Bricksforge WordPress Plugin CVE-2026-85097 Actively Exploited for Unauthenticated PHP Code Execution
Active exploitation of a critical vulnerability in the Bricksforge WordPress plugin is allowing unauthenticated attackers to upload and execute arbitrary PHP code on vulnerable sites, according to vulnerability research organization Patchstack. The flaw, tracked as CVE-2026-85097, affects Bricksforge versions up to and including 3.1.8.9 and is fixed in version 3.1.8.10. Key Points Patchstack reported active attacks exploiting a critical Bricksforge…
Daiichi Kosho Says Contractor Malware Put 8.7 Million Customer and Employee Records at Risk
Malware on a contractor’s computer may have put more than 8.7 million customer and employee records associated with Daiichi Kosho at risk, the company said. Daiichi Kosho said it had not confirmed data theft or leakage, and that its own systems were not breached. Key Points The potentially affected records include about 8.63 million customer records and 93,000 employee records.…
Apple iOS P7 DarkSword Exploit Kit Steals Keychain and Wallet Data via CVE-2025-24201
iVerify disclosed P7 DarkSword, a newly identified version of the iPhone exploit kit, on October 9, 2026, after investigating an infected iPhone belonging to a financial-institution employee in August. The variant has a smaller on-device footprint than versions iVerify had previously observed and adds on-device theft of Keychain and cryptocurrency-wallet data, along with two-way communication with attacker infrastructure. Key Points…
Midnight Mimosa Malware Infects Thousands of Low-Cost MediaTek Android Phones
Midnight Mimosa malware has been found embedded in the firmware of some low-cost Android smartphones, giving attackers system-level control before buyers use the devices. Bitdefender researchers said the campaign affected thousands of phones across more than 150 countries over a two-year period, with the largest concentrations in Mexico, France, and Italy. Key Points The campaign affects low-cost, multi-brand Android phones…
FakeGit Malware Uses 17,610 GitHub Repositories to Deliver SmartLoader and StealC
The FakeGit malware campaign reactivated on October 4, using 17,610 GitHub repositories to distribute SmartLoader and, through it, the StealC infostealer, according to Apiiro researchers. The operation pushed more than 13,000 repositories in its first 34 hours, reaching a peak of 2,999 repositories in one hour. Key Points FakeGit returned on October 4 with a network of 17,610 repositories. The…
Oracle Health’s 2025 Breach Was Far Bigger Than Known – Nearly 20M Affected, New Filing Reveals
The Oracle Health data breach compromised personal and medical information belonging to nearly 20 million people after attackers accessed legacy Cerner systems in early 2025, Bloomberg reported alongside records from the Texas attorney general. The figure is far higher than earlier filings and patient notifications, while Oracle has not publicly disclosed the total number of affected individuals and declined to…
Samsung Galaxy S26 Compromised Three Times at Pwn2Own Ireland Using Zero-Days
The Samsung Galaxy S26 was successfully compromised three times on the second day of Pwn2Own Ireland 2026, following three separate Galaxy S26 compromises on the opening day. Researchers earned $232,500 on day two after demonstrating 45 distinct zero-day vulnerabilities across the competition. Key Points KAIST Hacking Lab, PetoWorks, and Mobile Hacking Lab each compromised the Galaxy S26 on day two.…
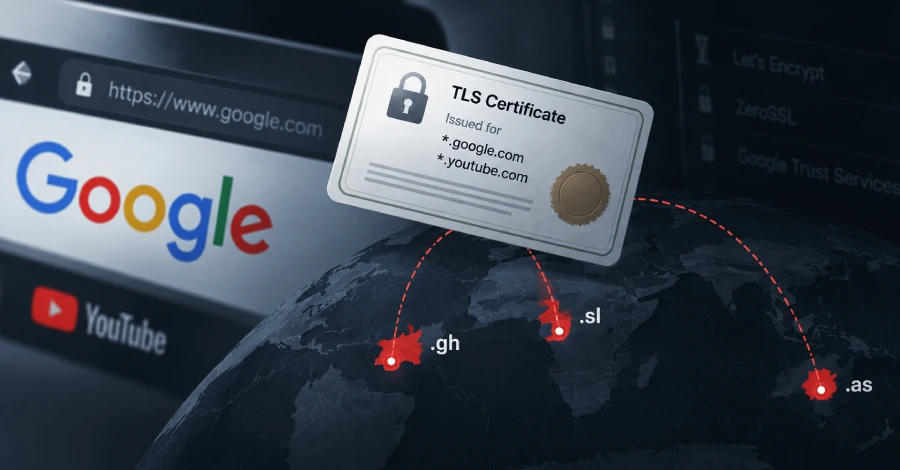
Google Chrome Blocks Unauthorized HTTPS Certificates After .gh, .sl and .as Registry Hijacks
Attackers hijacked the .gh, .sl and .as country-code top-level domain registries, altered authoritative DNS records and used the access to obtain unauthorized HTTPS certificates for several Google domains and domains belonging to other organizations. Google and Chrome blocked the identified certificates, coordinated their revocation with the issuing Certificate Authorities, and said the incident did not involve a compromise of Google’s…
Denmark’s Central Person Register Breach Exposes 8.8 Million CPR Records
Unauthorized parties accessed and exfiltrated personal data from approximately 8.8 million records in Denmark’s Central Person Register (CPR), including names, addresses and national identification numbers. The affected records cover living people, people who have moved abroad and deceased people, while authorities investigate how attackers misused a private company’s legitimate access to the registry. Key Points Approximately 8.8 million CPR records,…
LibreOffice Calc, Apache OpenOffice Calc Flaws Enable Java Code Execution: CVE-2026-63277, CVE-2026-59265
Vulnerabilities in LibreOffice Calc and Apache OpenOffice Calc can execute attacker-supplied Java code when a crafted spreadsheet is opened, without the macro-style warning or active-content prompt normally shown for macros. The Document Foundation released LibreOffice fixes on October 5, 2026, while Apache OpenOffice 4.1.16 and earlier remained affected pending version 4.1.17. Public proof-of-concept files and technical write-ups are available, although…
ShinyHunters Suspect Detained in Jordan, Reportedly Cooperating in FBI Employee Data Probe
An alleged ShinyHunters member detained in Jordan is reportedly cooperating with the FBI and international law enforcement, according to people familiar with the matter, as investigators seek to identify other members of the data-extortion operation. The case follows the reported detention of a 24-year-old Amsterdam man in the Netherlands and an investigation into claims that ShinyHunters stole FBI employee data,…
Apple CoreGraphics CVE-2026-86950 PoC Triggers iOS and macOS Crashes via Malicious PDFs
An Apple CoreGraphics proof-of-concept for CVE-2026-86950 now publicly reproduces a crash caused by a crafted PDF with an embedded font, while Apple has warned that the flaw may have been used in a targeted attack. Apple released patches on September 28, and the Cybersecurity and Infrastructure Security Agency added the vulnerability to its Known Exploited Vulnerabilities catalog the next day…

Microsoft Says Star Blizzard Phishing Targeted Over 100 Organizations With CosmicPulse Malware
Russian state-sponsored group Star Blizzard has used compromised legitimate websites and a malware-delivery technique Microsoft calls RedFlick in phishing campaigns that affected more than 100 organizations, primarily in the United States and United Kingdom, between January and August 2026. The campaigns targeted Ukrainian individuals and institutions, international nongovernmental organizations, think tanks, governments, financial institutions and other groups connected to support…

Attackers Used ChatGPT Custom GPTs to Install RATs on Dozens of Users’ Devices
Attackers used ChatGPT Custom GPTs and Google Sites to deliver a ClickFix social-engineering lure that persuaded victims to run a PowerShell command, leading to a multistage infection and installation of a remote access trojan (RAT), according to Huntress. The campaign was observed in late September 2026 and affected dozens of users, with the Huntress security operations center responding to at…
Attackers Exploited Two Citrix NetScaler Flaws Before Disclosure, Affecting More Than 100 Organizations
Two Citrix NetScaler vulnerabilities, CVE-2026-88771 and CVE-2026-88772, were actively exploited for weeks before their public disclosure, Citrix confirmed on September 27, 2026. CISA added both flaws to its Known Exploited Vulnerabilities catalog the same day, while the release of a proof of concept and root-cause analysis triggered mass “spray-and-pray” scanning against internet-facing NetScaler appliances. Key Points CVE-2026-88771 enables unauthenticated remote…
Critical Oracle PeopleSoft Flaw (CVE-2026-35273) Actively Exploited by UNC6240 to Deploy Backdoors
A renewed mass-exploitation campaign is targeting Oracle PeopleSoft Environment Management Hub servers through CVE-2026-35273, a critical unauthenticated remote-code-execution vulnerability with a CVSS score of 9.8. Google tracks the activity to UNC6240, a threat actor linked to ShinyHunters, and said attackers modified the exploit to bypass web application firewall rules before deploying web shells, backdoors and tunneling tools across multiple sectors.…
CISA Adds Exploited SharePoint RCE and MikroTik Flaws Enabling RouterOS Device Takeovers
SharePoint RCE vulnerability CVE-2026-65660 and MikroTik RouterOS vulnerability CVE-2026-67279 have been added to the U.S. CISA Known Exploited Vulnerabilities catalog after active exploitation was reported. Attackers are also chaining CVE-2026-67279 with the previously listed CVE-2026-86060 in an exploit chain called “MikroTrick,” which provides full unauthenticated administrative access to vulnerable RouterOS 7.x devices. Key Points CVE-2026-65660 affects Microsoft SharePoint Enterprise Server…