Cybersecurity News & Blogs:
Threats, Vulnerabilities & Security Guide

In todays connected world, cybersecurity is critical for individuals and businesses. CyberSecurityWaala covers the latest cybersecurity news, threats, vulnerabilities, cyber awareness, and security best practices to help you stay protected online with practical guides, real-world examples, and expert insights.

Today's Cyber Pulse
Live Feed • Synced 6 hours ago
Security News at a Glance

Critical flaws and active exploitation are dominating this cycle, with multiple vendors issuing urgent patches while attacks and credential-harvesting campaigns continue to escalate. SonicWall, Citrix, Atlassian and an unpatched LMCache bug are drawing active mitigation or exploitation attention, while malware campaigns including Overlord RAT via npm and PoeLLM crypto-mining botnet have infected thousands of systems. The FBI warns FortiBleed credential-harvesting remains active after tens of thousands of Fortinet credentials were collected, and AI is reshaping vulnerability discovery and policy debates even as phishing-resistant authentication remains vital.

Cert Fraud The Hacker News • Today

Registries Hijacked to Issue Google Domain Certificates

Attackers hijacked the registries for .gh, .sl and .as to request and obtain TLS certificates for Google-owned domains, enabling potential impersonation and man-in-the-middle attacks. This kind of registry compromise undermines trust in domain validation and can facilitate large-scale phishing or interception campaigns.

Risk Trend The Hacker News • 1d ago

CISO Data: Cyber Risk Has Shifted Inside Workflow

The Sixth Voice of the CISO report shows cyber risk is increasingly embedded in business workflows rather than just perimeter systems, highlighting a shift in where controls must be applied. Security teams will need to integrate controls into collaboration and developer tooling to reduce this inside-the-workflow risk.

Attack Cybersecurity Dive • 2d ago

Series of Attacks Tests US Cyber Resilience and Oversight

A sequence of cyber incidents has put U.S. cyber resilience and oversight mechanisms under strain, exposing gaps in preparedness and interagency coordination. The events underline the need for stronger governance and faster operational responses to complex campaigns.

Critical CVE The Hacker News • 1d ago

SonicWall Patches CVSS 10.0 Pre-Auth SSRF in SMA1000

SonicWall released a critical patch for a CVSS 10.0 pre-auth SSRF vulnerability affecting SMA1000 appliances that could allow unauthenticated access or code execution. Organizations running affected devices should apply vendor updates immediately to prevent easy remote compromise.

Zero-Day The Hacker News • 1d ago

Unpatched LMCache Flaw Allows Unauthenticated Remote RCE

Researchers disclosed a critical LMCache vulnerability that enables unauthenticated attackers to execute code remotely, and it remains unpatched. Active exploitation potential makes rapid mitigation and monitoring essential for affected deployments.

Exploitation The Hacker News • 1d ago

Atlassian Data Center Flaw Exploited Within Two Hours

A Data Center vulnerability in Atlassian products drew exploitation attempts within two hours of public disclosure, demonstrating how fast threat actors weaponize disclosed flaws. Administrators should apply vendor guidance and harden exposures to reduce immediate risk.

Patch Cybersecurity Dive • 3d ago

Citrix Issues Patch for Third Exploited NetScaler Flaw

Citrix released a patch addressing a third NetScaler vulnerability that has seen active exploitation, emphasizing continued targeting of the appliance family. Enterprises using NetScaler/ADC should prioritize installing the update and reviewing logs for signs of prior compromise.

Infostealer The Hacker News • 1d ago

Malicious npm Packages Deliver Overlord RAT and Stealer

Eight npm packages were found delivering the Overlord RAT and an information stealer and have been downloaded over 40,000 times, exposing developer environments and CI systems. This supply-chain abuse shows how package ecosystems remain a lucrative vector for persistent remote access and data theft.

Botnet The Hacker News • 1d ago

PoeLLM Malware Infects 3,400+ Servers to Grow Mining Botnet

PoeLLM malware has infected more than 3,400 servers to expand a crypto-mining botnet, leveraging compromised hosts for sustained mining operations. Large-scale server compromises like this increase operational costs for victims and can be repurposed for other malicious activity.

Credentials The Hacker News • 1d ago

FBI: FortiBleed Stole 86,644 Fortinet Device Credentials

The FBI warned that the FortiBleed credential-harvesting campaign has amassed 86,644 Fortinet device credentials and remains active, with attackers using the data to lock out legitimate users. Affected organizations should rotate credentials, review access logs, and apply vendor mitigations to restore secure access.

AI Tool Cybersecurity Dive • 2d ago

IBM AI Clearinghouse Finds Hundreds of Java Vulnerabilities

IBM's AI-powered vulnerability clearinghouse identified hundreds of Java flaws, demonstrating how machine-assisted tools can accelerate discovery of legacy vulnerabilities. While the findings can improve patch prioritization, they also increase the speed at which flaws may be weaponized if not remediated.

Policy Cybersecurity Dive • 3d ago

White House AI Task Force Faces Expertise and Partnership Gaps

The White House AI task force is encountering challenges around expertise and building partnerships, which may slow progress on national AI security and governance initiatives. Addressing those gaps is critical to shaping effective AI risk management and cross-sector collaboration.

AI Security Cybersecurity Dive • 3d ago

Modernizing Data Security With DSPM, AI and Fewer Tools

A sponsored report argues for modernizing data security using DSPM and AI to reduce tool sprawl and improve visibility across data workflows. Organizations evaluating data protection strategies should consider how AI-driven DSPM can centralize controls and reduce blind spots.

Phishing Cybersecurity Dive • 1d ago

Okta: Phishing-Resistant Authentication Still Essential Despite AI

Okta warns that AI does not change the singular importance of phishing-resistant authentication methods, stressing that strong MFA and phishing-resistant protocols remain the best defense. Organizations should prioritize deployment of phishing-resistant auth to mitigate credential theft amplified by AI tools.

Latest Posts

Recently added contents.

View all posts
Multi-Turn Prompt Injection That Actually Works on AI Chatbots
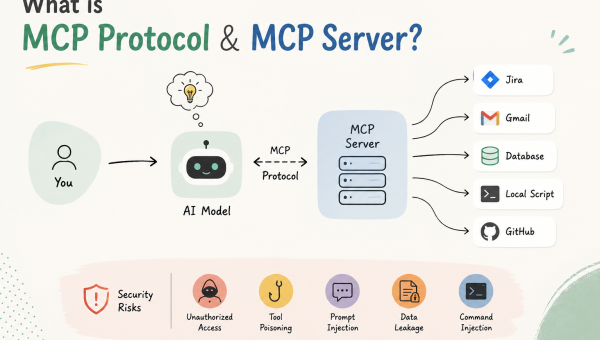
What is MCP Protocol and MCP Server? A Simple Guide for 2026

What is MCP Protocol and MCP Server? A Simple Guide for 2026

If you have been following the AI space lately, you must have come across the term MCP. It...
Is AI Deployment Actually Delivering the ROI You Planned For?

Is AI Deployment Actually Delivering the ROI You Planned For?

A lot of companies went into AI deployment with real expectations. Faster workflows, lower costs, better decisions. And...
Mythos Ready Is Just a Buzzword – Here’s the Proof

Mythos Ready Is Just a Buzzword – Here’s the Proof

Open any cybersecurity newsletter right now and you’ll almost certainly see the words “Mythos-ready.” Vendors are using it,...
Is Data Privacy in India a Joke? The Honest Answer in 2026

Is Data Privacy in India a Joke? The Honest Answer in 2026

Let me ask you something. When was the last time you actually read the privacy policy of an...
What Is a Phishing Attack? How It Works and How to Stay Safe

What Is a Phishing Attack? How It Works and How to Stay Safe

Phishing tricks people into clicking malicious links, opening files, sharing information, approving logins, or sending money. Learn how...
NIST Cybersecurity Framework: A Complete Guide to Modern Security Management

NIST Cybersecurity Framework: A Complete Guide to Modern Security Management

The NIST Cybersecurity Framework (CSF) gives organizations a practical way to understand, manage, and communicate cybersecurity risk. The...
LiteLLM Supply Chain Attack 2026: What Happened and What You Must Do Right Now

LiteLLM Supply Chain Attack 2026: What Happened and What You Must Do Right Now

On March 24, 2026, one of the most widely used AI gateway libraries got hit by a supply...
What is MCP in AI Security: Understanding Model Context Protocol Risks

What is MCP in AI Security: Understanding Model Context Protocol Risks

Anthropic introduced the Model Context Protocol (MCP) in November 2024. MCP gives AI applications a standard way to...
AI Scams Targeting Parents: How to Spot Them and Stay Safe in 2026

AI Scams Targeting Parents: How to Spot Them and Stay Safe in 2026

AI is making family impersonation scams harder to spot. Here is how voice cloning, deepfakes and fake emergency...
Vibe Coding Security Risks: Why AI-Generated Code Can Be Dangerous

Vibe Coding Security Risks: Why AI-Generated Code Can Be Dangerous

Vibe coding has changed how quickly people can build software. You describe what you want in plain English,...
AI Agent Hacking Itself Through Prompt Injection: What I Found

AI Agent Hacking Itself Through Prompt Injection: What I Found

So, I did something a little unhinged last week. I set up an AI agent, gave it a...
71 Malicious Claude Skills Found: The AI Plugin Marketplace is a Minefield

71 Malicious Claude Skills Found: The AI Plugin Marketplace is a Minefield

So I was going through my usual morning security feed when a headline stopped me cold. Straiker, a...
AI Deepfakes in Social Engineering: The New Face of CEO Fraud 2026

AI Deepfakes in Social Engineering: The New Face of CEO Fraud 2026

Imagine you are working in the finance team. You get a video call from your CEO. The face...