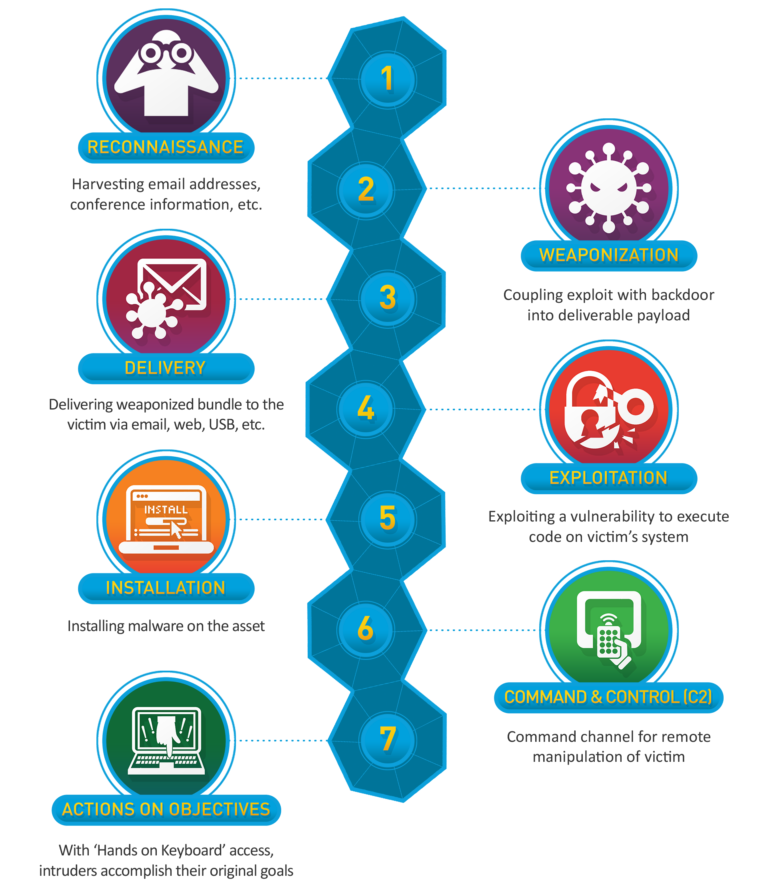
Most people learn the Cyber Kill Chain as seven simple steps: reconnaissance, weaponization, delivery, exploitation, installation, command and control, and actions on objectives. This makes the model easy to remember. But in real-world attacks, things are usually not that simple.
An attacker might repeat a step, skip one completely, or move through several activities at once. The model is still useful, though, because it gives defenders a simple question to work with: where can we stop the intrusion?
What Is the Cyber Kill Chain?
The Cyber Kill Chain is an intrusion model developed by Lockheed Martin as part of its Intelligence Driven Defense approach. It breaks an intrusion into seven broad stages, from reconnaissance through the attacker’s final objective. The important part is how you use the model: it is a high-level way to understand an intrusion, not a rule saying every incident will follow the same path.
That matters even more in modern environments. An attacker can get into a cloud service with stolen credentials, abuse a trusted software supply chain, or use legitimate administration tools without creating the neat sequence shown in a Kill Chain diagram. A phishing attack, for instance, may end with stolen credentials rather than a software vulnerability being exploited.
The 7 Cyber Kill Chain Stages at a Glance
| Stage | In simple terms |
|---|---|
| Reconnaissance | Finding information about the target |
| Weaponization | Preparing the tools or payload for the attack |
| Delivery | Getting the weaponized content to the target |
| Exploitation | Triggering a vulnerability or other condition that gives the attacker a foothold |
| Installation | Installing a payload or establishing persistence |
| Command and Control | Communicating with a compromised system |
| Actions on Objectives | Carrying out what the attacker came to do |
1. Reconnaissance
Before trying to get in, an attacker needs to understand the target. That can mean collecting information about employees, domains, IP addresses, exposed services, technologies, email addresses and the organization’s public-facing infrastructure.
Some reconnaissance is passive. An attacker can study a company’s website, public documents, social media, DNS records, certificate information or leaked credentials without touching the target directly. Other reconnaissance is active, such as scanning internet-facing systems for open ports and services.
This is where the public attack surface becomes important. An old subdomain, forgotten test server or exposed administration panel may not look serious to the people who built the environment. To an attacker, it can reveal useful information about what is running and where to look next.
2. Weaponization
Weaponization is the preparation of the material the attacker intends to use. In the original model, this could mean pairing malicious code with an exploit or creating a document designed to exploit a particular weakness.
It does not necessarily mean writing malware from scratch. An attacker may modify an existing tool, prepare a malicious document, package an exploit or build a payload for a particular target.
There is a catch, though: much of this work happens outside the victim’s environment. A security team may never see the attacker preparing the payload. The first useful evidence can appear only when that payload reaches an employee, application or device.
3. Delivery
Delivery is how the attacker gets the prepared material to the target. A phishing attachment or malicious link is an obvious example, but delivery can also involve a compromised website, removable media, a malicious software update or an attack against an exposed service.
Delivery and exploitation are easy to mix up. A malicious attachment arriving in an employee’s inbox is delivery. If opening it triggers a software vulnerability and causes code to run, that is exploitation. If the attachment instead relies on the user being tricked into taking an action, the mapping is less straightforward.
The distinction matters during an investigation because the controls are different. Email security may stop the delivery, while endpoint protection may detect what happens after the file is opened.
4. Exploitation
Exploitation is the point where the delivered material triggers a vulnerability or another condition that gives the attacker the access or capability they need. If the terms vulnerability and exploit are new to you, think of the vulnerability as the weakness and the exploit as the method used to take advantage of it. A vulnerable application processing a crafted request is a straightforward example.
Modern incidents are not always this clean. An attacker who already has a valid username and password may not need to exploit a software vulnerability at all. In that case, the traditional exploitation stage is difficult to map directly to what happened.
That is why I would use the Kill Chain to make sense of an intrusion, rather than force every incident into the same seven boxes.
5. Installation
After gaining access, an attacker may install a malicious payload or establish a way to maintain access. Depending on the attack, this can involve malware, a service, a scheduled task, a startup mechanism or another persistence technique.
But installation is not guaranteed. An attacker using stolen credentials or legitimate operating-system tools may never install a traditional program. The absence of a new executable does not mean the system is clean.
This is where endpoint and identity telemetry become important. Process creation, service changes, scheduled tasks, authentication events, registry changes and other system activity can help investigators work out how access was maintained.
6. Command and Control
Command and control, usually called C2, is the communication an attacker uses to interact with a compromised system. Depending on the technique, this may involve HTTP or HTTPS, DNS, another network protocol, or a legitimate online service.
Looking for C2 is not as simple as finding one suspicious IP address. An analyst may look for repeated outbound connections, unusual DNS requests, regular beacon-like traffic, or a machine talking to infrastructure that has no obvious business purpose. One event may be harmless. A pattern across several events is usually more interesting.
Attackers can also change infrastructure or use several communication channels. MITRE ATT&CK documents multi-stage C2, where different channels can be used at different points in an intrusion. That is one reason endpoint, DNS, proxy and network telemetry are more useful together than in isolation.
7. Actions on Objectives
This is where the attacker carries out the reason they targeted the environment in the first place. The objective depends on the incident.
- Steal sensitive information
- Move laterally through the environment
- Deploy ransomware
- Modify or destroy data
- Maintain access for espionage
- Disrupt systems or operations
The phrase “actions on objectives” is deliberately broad. A ransomware operator, an espionage group and a financially motivated attacker may reach the same stage but do very different things.
Where Can Defenders Break the Attack?
This is where the Kill Chain becomes more useful than a diagram in a training slide. An organization does not have to detect an attacker at the first stage. It has several opportunities to interrupt the intrusion.
| Stage | What defenders might see | Useful controls or telemetry |
|---|---|---|
| Reconnaissance | External scanning, enumeration or unusual discovery activity | Attack-surface management, WAF and network monitoring |
| Weaponization | Threat intelligence about exploit or payload preparation; malicious files appearing in campaigns | Threat intelligence, malware analysis and email security |
| Delivery | Malicious links, attachments, downloads or suspicious inbound traffic | Email filtering, web filtering and application controls |
| Exploitation | Exploit attempts, abnormal process execution or unusual application behavior | Patch management, WAF, EDR and exploit protection |
| Installation | Unexpected services, scheduled tasks, startup changes or binaries | EDR, application control and endpoint hardening |
| Command and Control | Beaconing, unusual DNS activity or suspicious outbound connections | DNS security, proxy controls, network monitoring and EDR |
| Actions on Objectives | Unusual file access, lateral movement, encryption or large data transfers | Identity monitoring, segmentation, DLP, backups and incident response |
A Simple Example: How a Phishing Attack Can Move Through the Kill Chain
Consider a simple scenario. An attacker wants access to an employee’s Microsoft 365 account.
The attacker identifies the organization, finds employee names and learns which login service the company uses. That is reconnaissance.
Next, the attacker prepares a convincing phishing page and the email used to send it. That is the weaponization stage.
The message then reaches the employee’s inbox. That is delivery.
Here the model starts to become less tidy. There may be no software vulnerability at all. The attacker is relying on the victim to enter credentials into a fake login page, so this activity does not map neatly to the original exploitation stage.
There may be no installation at all. The attacker can use the stolen credentials directly.
Depending on what happens next, the attacker may use an established service or other infrastructure to continue operating. That is where command and control may come into the picture.
The attacker may search email, steal information, register additional access, or use the compromised account to target other employees. Those are the actions on objectives.
This example shows both the value and the limitation of the model. The Kill Chain helps us describe the attack path, but it does not always provide a perfect box for every activity.
What the Cyber Kill Chain Does Not Capture Well
The original model is useful, but today’s environments are more complicated than the endpoint-focused attacks that shaped many early intrusion models.
Consider an attacker who steals a session cookie and signs in to a cloud service. There may be no malware installation. A supply-chain compromise can also give an attacker a trusted path into an environment rather than a conventional delivery stage. Living-off-the-land techniques can make the attacker look more like a legitimate administrator because the tools are already present.
Attackers can also move back and forth. They may gain access, lose it, steal another credential, return through a different account and then continue. A real incident timeline can look much messier than a seven-step diagram.
That does not make the Kill Chain obsolete. It means you should know what question it is answering. It is good for understanding the broad path of an intrusion. It is not a complete inventory of every technique an attacker may use.
Cyber Kill Chain vs MITRE ATT&CK
The two frameworks are often mentioned together, but they are not interchangeable. MITRE explains the relationship between ATT&CK and the Cyber Kill Chain in its framework FAQ.
The Cyber Kill Chain gives you a high-level view of an intrusion. MITRE ATT&CK provides much more detail about adversary tactics and techniques based on observed real-world behavior. MITRE describes the two as complementary: the Kill Chain uses ordered phases to describe high-level objectives, while ATT&CK describes adversary behavior at a lower level of detail and does not require tactics to occur in a fixed sequence.
A practical way to think about the difference is this:
| Question | Useful model |
|---|---|
| Where is the attacker in the broad intrusion? | Cyber Kill Chain |
| What specific technique did the attacker use? | MITRE ATT&CK |
| What telemetry could help detect the behavior? | ATT&CK data sources and your security tooling |
| Where did the organization interrupt the intrusion? | Cyber Kill Chain |
Using both gives a better picture than treating either framework as a complete answer.
Real-World Example: WannaCry
WannaCry is a useful example because it shows how quickly exploitation and propagation can turn a vulnerability into a large-scale incident.
In 2017, WannaCry exploited a Windows SMB vulnerability associated with MS17-010. Microsoft’s MS17-010 security bulletin documented the underlying vulnerabilities and fixes, while CISA’s advisory documented WannaCry and other malware exploiting the same SMB vulnerabilities.
Once a vulnerable system was compromised, WannaCry could spread to other vulnerable systems. That makes the incident a practical reminder that vulnerability management is not just about fixing a theoretical security problem. A remotely exploitable weakness on a networked system can become a path to rapid propagation.
WannaCry also shows why it is better not to force an incident into seven perfectly separated boxes. Exploitation and propagation happened quickly. The framework helps explain the broad attack path, but the real event was more complicated than a clean diagram.
Real-World Example: Target
The 2013 Target breach shows a different kind of attack path. According to a U.S. Senate Commerce Committee staff report, attackers used credentials associated with a third-party HVAC vendor to gain an initial foothold and then moved deeper into Target’s environment. The report also described missed opportunities involving malware alerts, network isolation and data exfiltration.
That makes Target particularly useful when thinking about the Kill Chain. The initial compromise was not the end of the story. There were additional opportunities to detect the attackers after they had entered the environment.
The lesson is broader than “third-party access is dangerous.” Security teams also need to think about what a compromised account or connection can reach, what unusual activity will generate an alert, and whether sensitive systems are sufficiently isolated.
How Security Teams Can Use the Cyber Kill Chain
A security team can use the model during threat hunting, incident response and security planning.
During threat hunting, the stages can help analysts ask what an attacker would likely need to do next. During incident response, they can help organize the timeline and identify where the intrusion was detected or missed. During security planning, they can expose gaps where the organization has little visibility or few controls.
Telemetry is what makes this practical. Depending on the environment, useful sources can include DNS logs, firewall and proxy records, endpoint detection data, authentication logs, cloud audit logs, application logs and file-access events.
The goal is not to collect every possible log. The better question is whether the available telemetry can answer the basics: How did the attacker get in? What did they execute? Which account or system did they use? Where did they communicate? What did they access? And what were they trying to accomplish?
Lockheed Martin has also described using the Kill Chain to identify defensive gaps by mapping countermeasures and available data to each stage. That is a practical use of the model because it turns the framework into a way of asking where an organization can detect, deny or disrupt an intrusion.
What the Kill Chain Gets Right and Where It Falls Short
The strongest part of the Cyber Kill Chain is its simplicity. It gives a security team a common way to talk about an intrusion without starting with a long list of individual techniques.
Its weakness is the same thing: simplicity. Modern attacks can involve identity abuse, cloud APIs, trusted software, stolen sessions and legitimate administration tools that do not fit neatly into the original sequence.
So I would use the Kill Chain as a starting point, not as the entire investigation. Use it to understand the broad attack path, then bring in MITRE ATT&CK and your endpoint, network, identity and cloud telemetry to work out what actually happened.
Final Thoughts
The Cyber Kill Chain is still a useful way to explain how an intrusion develops, especially when someone is learning cybersecurity. Its biggest strength is that it shifts attention away from the moment of compromise and makes you look at the steps around it.
But I would not use it by itself to analyze a modern incident. Cloud attacks, identity abuse, supply-chain compromises and living-off-the-land techniques can make the seven stages much less obvious.
For me, the best way to use the model is as a starting point. Use it to understand the broad attack path, then use more detailed frameworks such as MITRE ATT&CK, together with endpoint, network, identity and cloud telemetry, to understand what actually happened and where the next attack could be stopped.