The OpenSSH flaw dubbed “*sshole” can let attackers log in to some Alpine Linux and other musl-based...
Mayank Mehra
Mayank Mehra is a cybersecurity professional with 8+ years of hands-on experience in application security, penetration testing, vulnerability assessment, and AI security. He holds CEH, CAPEN, and CRTP certifications and specialises in identifying and mitigating security risks across applications and AI-powered systems.
AI security risks are weaknesses that can affect AI-powered applications, Large Language Models (LLMs), Retrieval-Augmented Generation (RAG)...
Debian and Ubuntu have published advisories for CVE-2026-109518, an APT flaw that lets an attacker on the...
Binance said a fake job interview campaign led to the Oct. 29, 2026 Binance hack, a security...

Attackers are actively exploiting a critical Siemens IoT2050 flaw, CVE-2026-58115, on SIMATIC IoT2050 Advanced devices, according to...
The FBI said North Korea stole more than $6 billion in virtual assets from Binance on or...
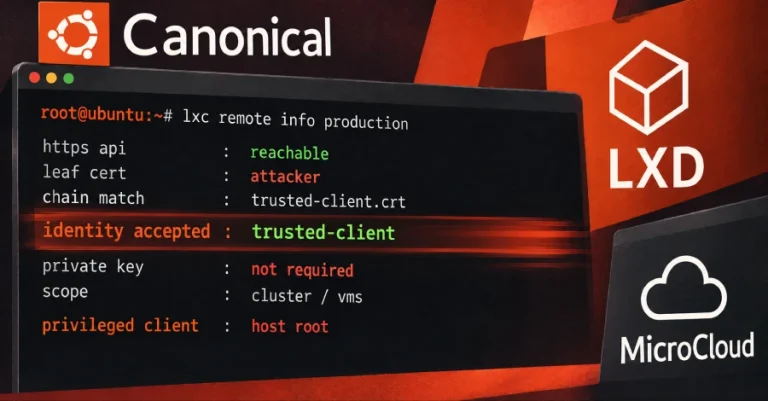
Canonical has disclosed a critical authentication-bypass vulnerability in LXD and MicroCloud that lets an attacker impersonate a...
October 21, 2026 started like any other Wednesday for most web administrators. By afternoon it had turned...
A previously undocumented UEFI bootkit called BlackX was used in a campaign targeting diplomatic agencies in Tajikistan,...
A critical Pillow vulnerability can let attackers run operating-system commands on a server when they control the...